Home/For accountants/AML compliance and audit trail
Doxxi for accountancy firmsAML compliance with a complete audit trail per client.
A risk score per client, review dates that follow the score, and proof of every check. When the ITAA or a supervisor asks, the evidence is already in the file.
In short
Compliance proven by the system
- Identification
- UBO and risk
- Who did what, and when
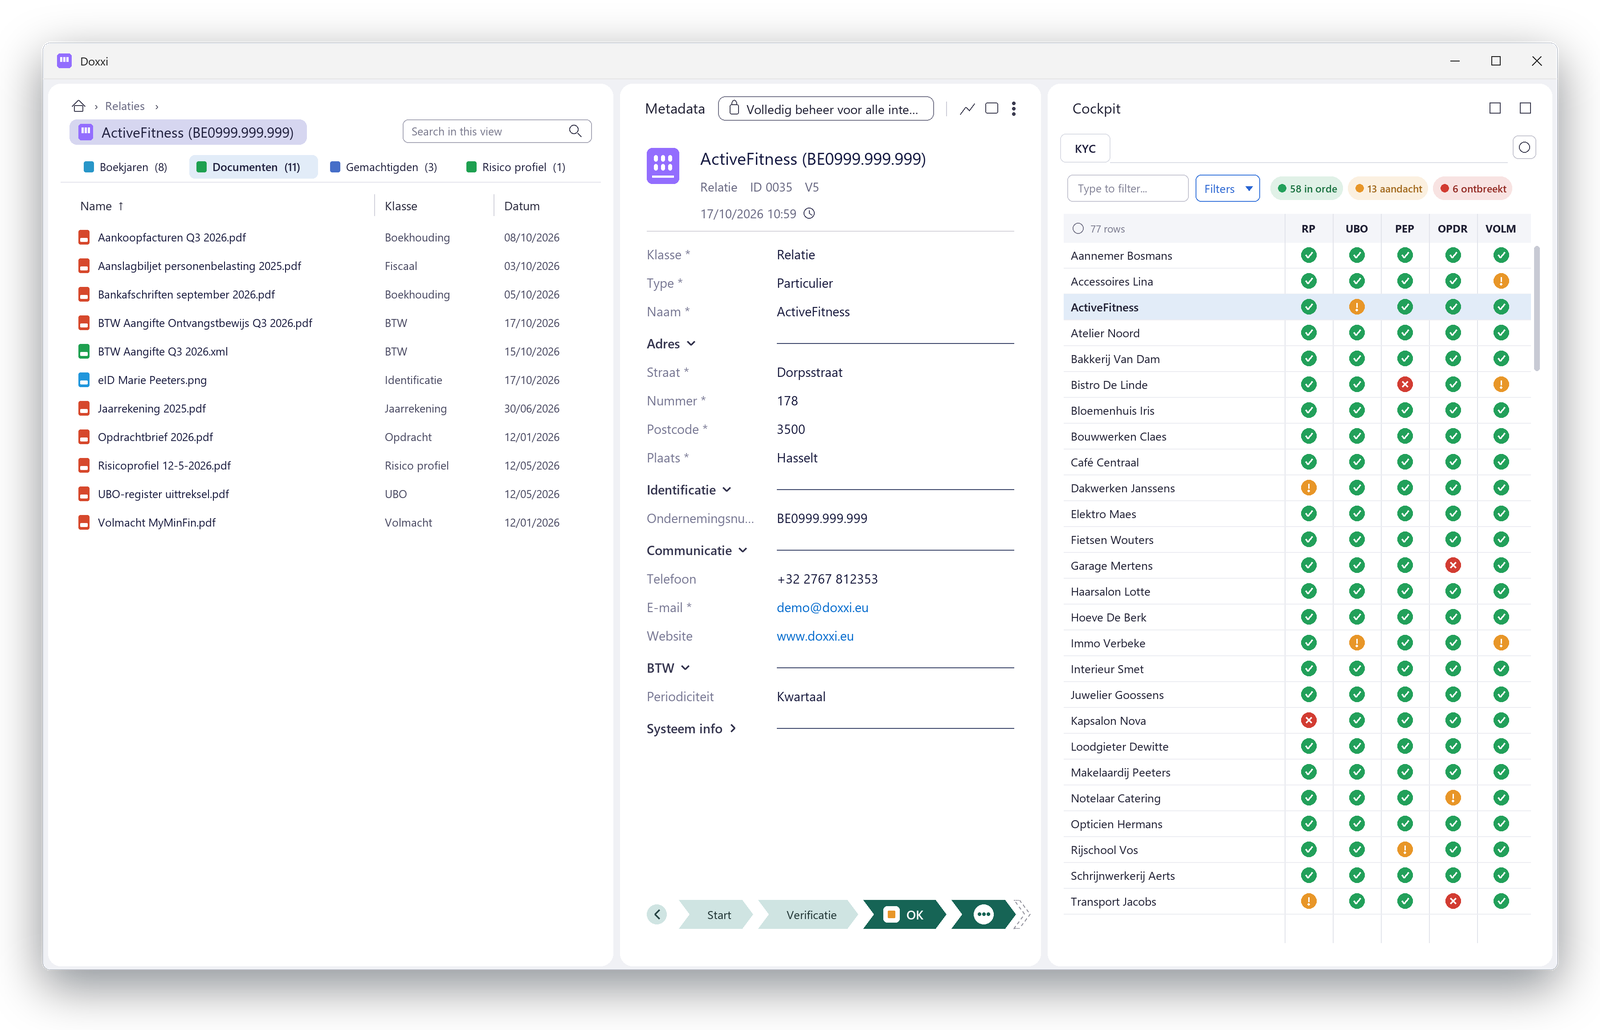
Doxxi records every AML step as part of the client file: identification, UBO check, risk assessment, approval and review. M-Files logs who did what and when, so compliance is proven by the system instead of reconstructed afterwards.
Proof that is missing when you need it
AML checks are often done, but not documented in one place. When a reviewer asks for evidence, your team digs through mailboxes and spreadsheets to rebuild what happened.
Hover over or tap a card to see the Doxxi way.
Checks done, proof scattered
The proof in the file
For an ITAA or supervisory check, the complete trail per client is one click away.
Different interpretations per file manager
One method for every file
Four categories give a low, medium or high risk score per client.
Reviews that are forgotten
Reviews that plan themselves
Review dates follow the score: every year or every three years.
Retention rules applied by memory
Retention applied automatically
Retention rules are set per document type and applied automatically. Documents are flagged for review or deletion when their period ends.
Compliance as part of the daily file
Score the risk
Four categories give a low, medium or high risk score per client.
Approve
The file manager approves the assessment. The approval is logged.
Review on time
Review dates follow the score: every year or every three years.
Show the trail
For an ITAA or supervisory check, the complete trail per client is one click away.
What the audit trail records
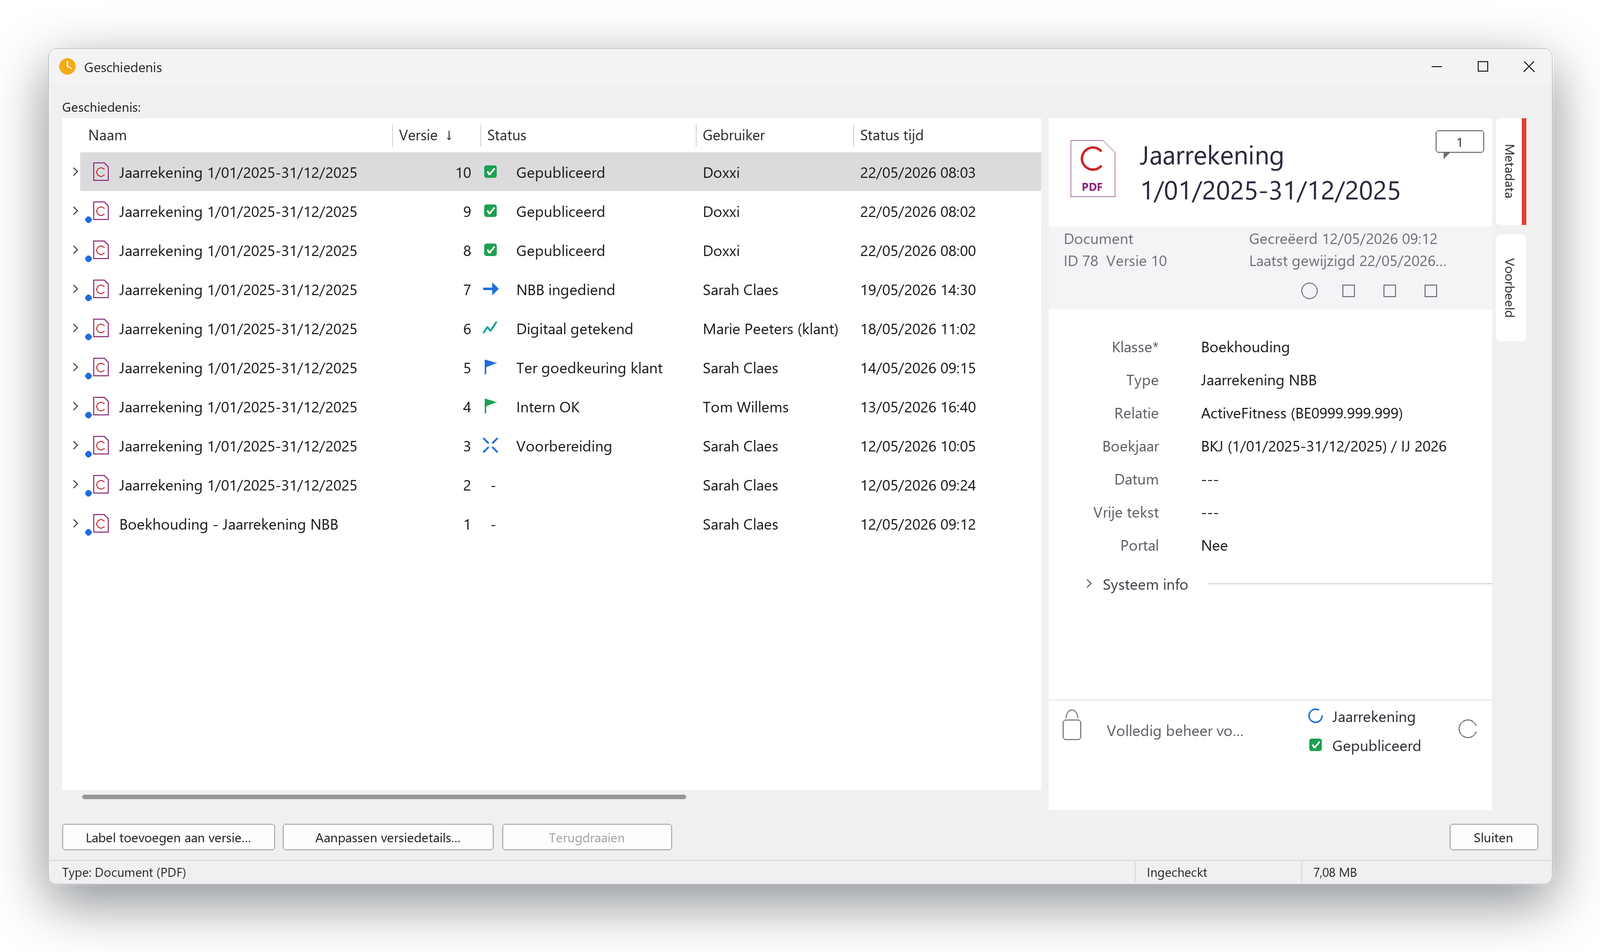
Built on M-Files: every document action is logged automatically, without manual work.
- Identification and UBO checks
- Risk assessments and approvals
- Review dates
- Signed engagement letters
- GDPR retention per document type
Questions
Which professional standards does Doxxi support?
Doxxi is configured to the documentation, retention and audit requirements of the ITAA in Belgium, the NBA in the Netherlands and the OEC in Luxembourg.
What does the audit trail show?
Every document action with timestamp, user and version: who created, changed, approved or viewed what, and when.
How is GDPR retention handled?
Retention rules are set per document type and applied automatically. Documents are flagged for review or deletion when their period ends.
Other Doxxi features for accountants
Digital signatures via Penneo
Engagement letters signed with itsme or eID, filed automatically.
Read moreMake your next review a formality
Book a one-hour demo. We show Doxxi based on your own document flows.